DevOps, hosting and maintenance for web applications We run what we ship
ANTASY IT (a.it) deploys, hosts and maintains the web applications we build: Linux servers with nginx, supervised processes, Cloudflare in front and monitoring we watch ourselves. The TSS Company ERP, SOLARP for Thyna Solar, the ESPAMED website and the Key Brothers store are deployed and supervised by us from Sfax, and SOLARP’s database and attachments are backed up on a schedule.
- Servers
- Linux · nginx · pm2 / systemd
- Edge
- Cloudflare · TLS end to end
- Running at
- TSS Company · Thyna Solar · ESPAMED · Key Brothers
- Last reviewed
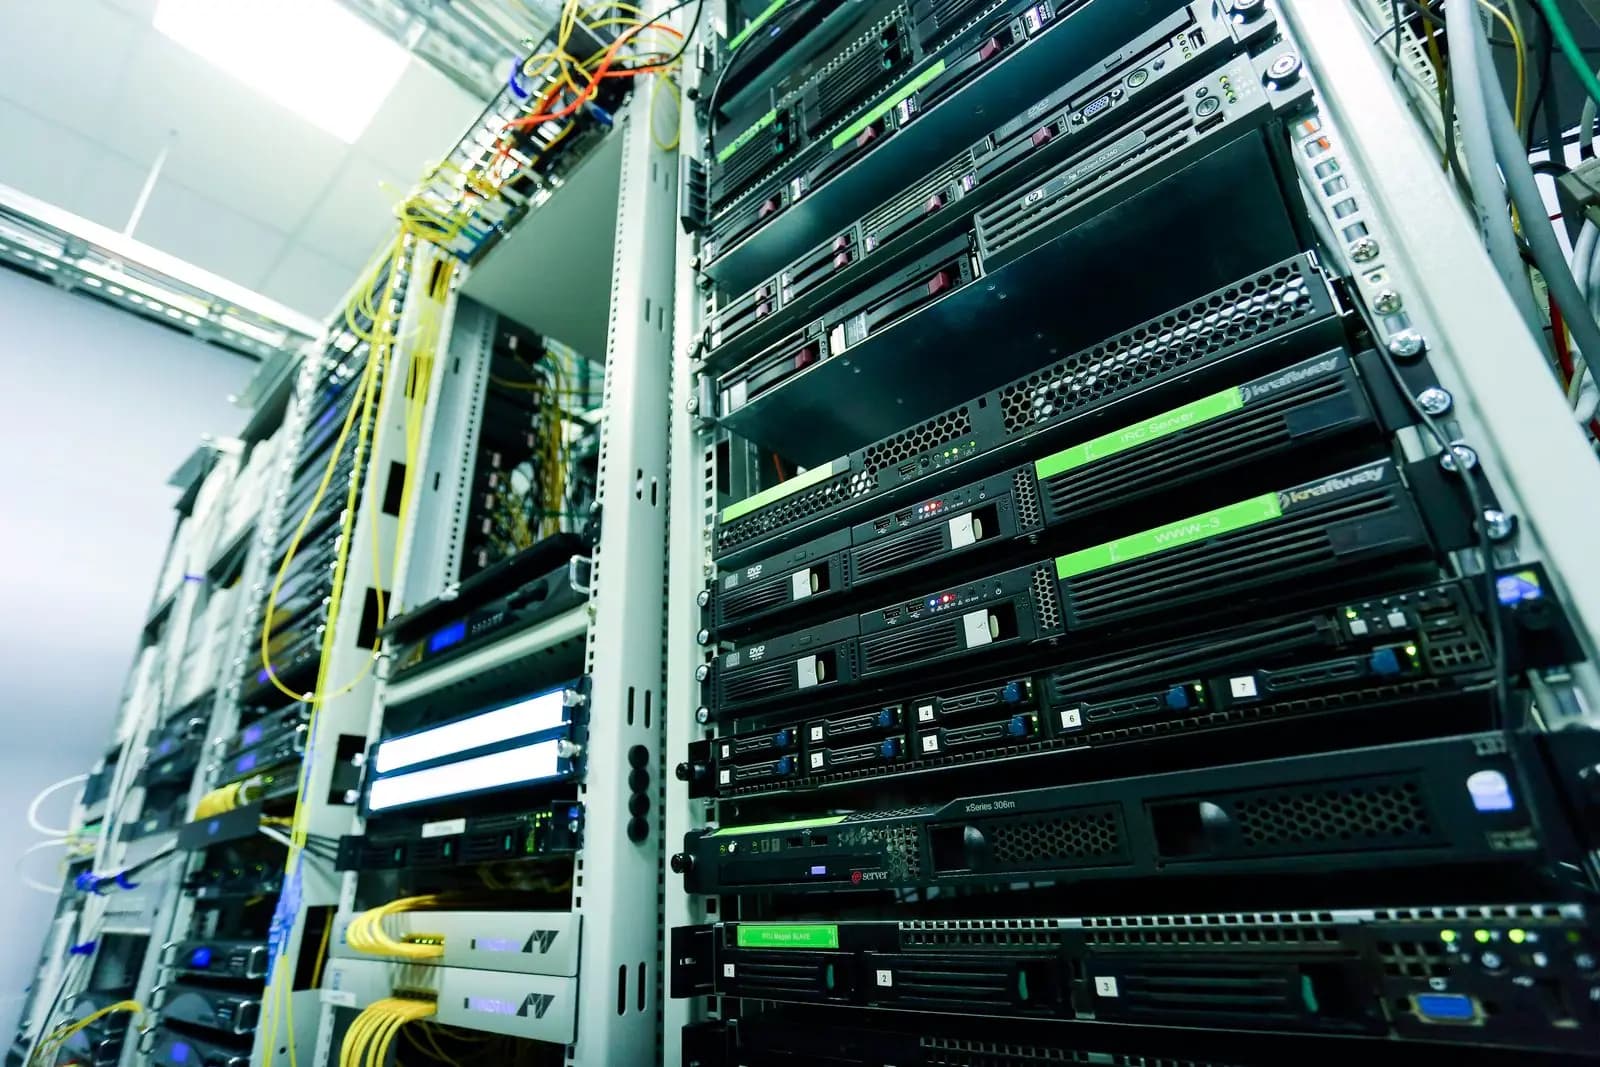
Deployed, monitored, maintained: your applications stay online.
Overview
What does “we run what we ship” mean?
It means the team that builds an application also deploys it, hosts it, backs it up, monitors it and fixes it. Nobody receives a zip file and a goodbye. ANTASY IT operates the applications it delivers on Linux servers behind Cloudflare, so the people who answer an incident are the people who wrote the code.
Most of the trouble in a web application’s life happens after launch: a certificate expires, a disk fills up, a framework publishes a security fix, a CDN serves last month’s page, a process runs out of memory at night. None of it is visible in a demo. All of it decides whether your team trusts the software.
Running what we ship is also an incentive. When we are the ones woken by a failure, we build applications that fail less, log what matters and recover on their own where they can.
What is included
What do hosting and maintenance include?
These are the building blocks we put in place for the applications we run. The exact scope is written down per application.
Deployment
Releases built and checked before they replace the running version, then checked again on the live address right after the switch.
Servers
Linux servers, with nginx in front of each application and Cloudflare in front of nginx.
Supervision
Processes run under pm2 or systemd and restart automatically if they crash, with a memory ceiling where an application needs one.
Cloudflare
DNS, TLS from the visitor to the origin with origin certificates, caching rules and protection at the edge.
Backups
Where the scope includes them: scheduled database dumps named with their date, uploaded files saved alongside, and each dump read back by the restore tool.
Monitoring
Our own dashboard: server health, processes, traffic and errors read from nginx logs, and a forecast of when each disk will be full.
Updates
Security fixes for frameworks and dependencies, planned and checked on a build before they reach production.
Secrets
Credentials in server-side environment files with restricted permissions, never in the code repository or the browser.
Changes
Fixes and small evolutions planned like any other work, by the team that knows the code.
From production
What have we learnt running applications in production?
Three problems we met on our own servers, and what we changed. This is the kind of knowledge a hosting contract should buy.
Why did a CDN keep serving an old page?
Next.js marks pre-rendered pages as cacheable by shared caches for a year by default. Behind Cloudflare, old pages could outlive a deployment. On ESPAMED’s site, nginx now replaces that header with one that forces revalidation, static files are versioned per deployment, and the stale entries were purged once.
Why did security headers vanish on some paths?
In nginx, a single add_header inside a location block silently drops every header inherited from the server block. One rule for caching was enough to remove the security headers from that path. We now include the shared headers in every location that adds its own.
Why did a service worker stop working behind the CDN?
Some edge bot-protection features inject a script into HTML pages. That injection breaks a strict Content Security Policy and interferes with service workers. We now check which edge features are enabled for each site before enabling a strict policy or offline support.
More on these choices in Next.js in production.
Monitoring
How do we monitor the applications we host?
With our own monitoring dashboard. A collector stores server health, process states and traffic read from nginx logs in a PostgreSQL database; incidents open when the share of server errors jumps or when the disk trend says it will soon be full. ANTASY IT sees every application it hosts on the same screen.
- Errors
- The share of server errors per site, computed from nginx logs over short windows; a jump opens an incident.
- Disk forecast
- A trend computed on hourly averages with the median of slopes, so a one-off jump such as a new swap file does not turn into a false alarm.
- Restarts
- A restart requested from the dashboard is queued, then executed by a separate service after checks; the web interface itself never holds system rights.
- Read-only web side
- The dashboard’s web application only reads the monitoring database; collection runs in its own process.
Backups
How are backups organised?
For the applications we back up, SOLARP and our own Made in Tunisia platform among them, the database is dumped on a schedule into a dated file, uploaded files are copied alongside, and each new dump is read back by the restore tool. ANTASY IT sets frequency and retention per application and states them in the scope.
Naming dumps by timestamp sounds trivial. It is the difference between restoring yesterday’s state and discovering that the last good copy was replaced by a test run, which is why SOLARP’s file names carry the time as well as the date. The same care applies to files outside the database: a restored database without its attachments is only half a restore.
Running today
Which applications do we run today?
Four companies on our logo wall have their software deployed, hosted and supervised by us, from business tools used all day to public websites. What each contract covers, backups included, is written per application.
TSS Company
The TSS Company ERP and its workshop module: a Strapi 5 API and a Next.js interface on PostgreSQL, deployed, supervised and maintained by us.
Thyna Solar
SOLARP, our CRM for PV installers: its database is dumped on a schedule into timestamped files, its uploaded attachments are copied alongside, and demonstrations use a separate database.
ESPAMED
The ESPAMED website (espamedical.com), a Next.js site running as a supervised process behind nginx on our servers.
Key Brothers
The Key Brothers online store, hosted on our servers and kept up to date by the team that built it.
Taking over
Can we take over an application built by someone else?
Yes, after an audit. The steps below are how we approach it; we tell you what we find before we promise anything.
01
Audit
Code, build, dependencies, server and data: what runs, what is outdated, what is missing.
02
Prepare
A server set up our way: nginx, supervision, backups and monitoring, before any switch.
03
Migrate
Code and data copied, then checked on a test address with your team.
04
Switch
DNS moved behind Cloudflare at an agreed time, with the old server kept until the new one is confirmed.
05
Run
Monitored, backed up and updated like the applications we built ourselves.
Stack and limits
Which tools, and what do we not promise?
The tools are deliberately ordinary and well documented: open-source Linux, nginx, Node.js, PostgreSQL, pm2 or systemd, with Cloudflare in front.
In production
- Linux
- nginx
- pm2
- systemd
- Node.js
- PostgreSQL
- Cloudflare
No invented uptime figure
This page does not publish an availability percentage or response time. Those numbers only mean something when they are measured and written into a contract, and we would rather agree them with you than display a figure we cannot show you the data for.
FAQ
Hosting and maintenance questions
Do you host websites too, or only business applications?
Both. The same setup runs business applications such as the TSS Company ERP and SOLARP for Thyna Solar, and websites such as ESPAMED’s and the Key Brothers store: supervised processes behind nginx and Cloudflare. On ESPAMED’s site, nginx also forces cache revalidation so a change shows at once. The scope written for each site says what else is included.
What does Cloudflare protect against?
Placed in front of the server, Cloudflare hides the origin’s address, absorbs traffic floods, encrypts connections and caches static files close to visitors. Its bot and firewall rules filter part of the abusive traffic. It does not fix weak passwords or vulnerable code, which is why updates and server hardening remain part of the job.
How do you deploy without breaking production?
A release is built and checked before it replaces the running version, and the live application is checked again right after the switch. Pages send revalidating cache headers and static files are versioned, so visitors get the new version after a deployment instead of a mix of old and new files.
What does maintenance include?
Security and dependency updates, monitoring, backups, incident handling and small fixes, by the team that wrote the code. The exact scope, including what counts as a small change and what becomes a new project, is written down for each application, so nobody discovers the limits during an incident.
Do you guarantee a level of availability?
We do not publish an availability percentage on this site. A figure only means something when it is measured and written into a contract, so we discuss targets, measurement and response times with you for each application. What we can show is how our monitoring works and what it watches.
How are passwords and API keys handled?
They live in environment files on the server with restricted permissions, and never in the code repository, the browser or shared documents. When a key must change, it changes in one place. Screenshots and documents we produce never show server or device addresses.
An application that must stay up? Let’s talk about running it
Tell us what it runs on today and who looks after it. We answer with what an audit would cover.